Is Claude Team SOC 2 Compliant?
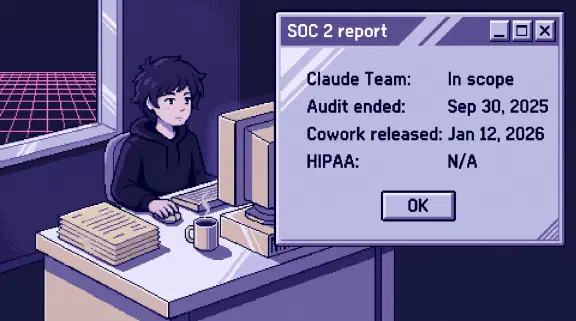
Yes. Anthropic’s Trust Center lists Claude Team as in scope for SOC 2 Type 2. It marks HIPAA as N/A for Team, so that answer is no.
The catch is in the dates. The latest report Anthropic publishes covers October 1, 2024 to September 30, 2025. Cowork’s first release came on January 12, 2026. So a Claude Team seat today includes a feature that didn’t exist during the audited period. Write “all of it is SOC 2 audited” on a customer’s questionnaire and you’re claiming more than the published report shows.
I haven’t tested any of this or read the full SOC 2 report, which sits behind an access request. This comes from public pages and the public SOC 3 report, read on October 30, 2026. I set up Claude Team for small companies, so I have a stake. None of this is legal advice.
Is Claude SOC 2 compliant?
It depends on the product. Here is the Trust Center’s table, shortened:
| Product | SOC 2 Type 2 | HIPAA |
|---|---|---|
| Claude Team | Yes | N/A |
| Claude Enterprise | Yes | Yes |
| Anthropic’s API | Yes | Yes |
| Microsoft Foundry, hosted on Anthropic | Yes | Yes |
| Microsoft Foundry, hosted on Azure | “In-Process Q4 2026” | Yes |
| Amazon Bedrock, Google Vertex AI | Yes, for “the model itself and containers supplied to partners by Anthropic” | “Partner-Managed” |
| Free, Pro, Max, Ultra | Not listed | Can’t enable it |
The last row bites small companies. Anthropic’s certifications page says it’s about “our commercial products such as Claude for Work and the Anthropic API.” If two of your people do company work on personal Pro accounts, the Team checkmark says nothing about them. Your answer is true only once company work is on company seats.
Anthropic’s own FAQ says “our SOC 2 certification,” but the report is an auditor’s opinion about one period. On a questionnaire, write “audited” and give the dates.
What does Claude Team’s SOC 2 report actually cover?
It covers something called the “AI Services system,” and neither plan name appears in the SOC 3 report, the public 2025 report. “Team” and “enterprise” show up only as everyday words, such as “functional teams.” The Trust Center table is what connects that system to the plan you bought.
The report describes the system this way: “Anthropic’s web-based and native applications consist of a chat interface” plus an API. Claude Code gets one mention, in the list of things customers must handle themselves. The words “Cowork” and “connector” appear nowhere.
Here is what has shipped or changed since the period closed:
- Cowork started as a research preview on January 12, 2026, became generally available on April 9, and runs on Team plans.
- Hosting. The report names Google Cloud and AWS. The subprocessor list now also shows Microsoft Azure, “Products: All Products”.
- Vendors. The October 14 update added Parallel Web Systems and hCaptcha as subprocessors.
Cowork may be well run. The published audit still can’t be your evidence for it, because auditors can’t test a product that didn’t exist in the window.
Anthropic fills the gap with bridge letters. The resources page lists three from 2026, all behind the access request: August, “Oct 2026 Update” and “Oct 2026 New”. A bridge letter is “a document provided by a service organization (not the service auditor)”, and that CPA firm calls the comfort it gives “interim (and unverified)”. Treat one as the company’s own word.
What does a SOC 2 Type II report promise?
It promises that an auditor checked the controls over a whole period. In the report’s wording, Anthropic’s claim that its controls were “effective throughout the period” is “fairly stated, in all material respects.” That “throughout” is the Type II part. Someone checked over twelve months, against criteria for “security, availability, confidentiality, and privacy”.
It doesn’t promise any of this:
- The future. It warns that “the projection to the future of any conclusions about the effectiveness of controls is subject to the risk that controls may become inadequate because of changes in conditions”.
- Certainty. The assurance is “reasonable, but not absolute”.
- Accuracy. Processing integrity is one of the five categories in the standard, and it isn’t among the four here. If a questionnaire asks whether the report speaks to correct output, it doesn’t.
- The cloud underneath. “Our examination did not include the services provided by the subservice organizations”.
- Your company. SOC 2 on your vendor gives you no SOC 2 of your own.
The report also hands work back to you. Customers must make sure data they submit “complies with applicable laws, regulations, and the user entity’s own data governance policies”, provision and remove users, set up “MFA and single sign-on integrations”, and secure “the local environments where Claude Code is executed”. Notice and consent for people’s personal data are yours too, because the report treats Anthropic as the data processor. Be ready to show your half.
Is Claude Team HIPAA compliant?
No, and you can’t buy your way there on this plan. Anthropic’s HIPAA article says: “Team plans and individual plans (Free, Pro, Max, and Ultra) can’t enable HIPAA.” The Trust Center FAQ agrees: “Our BAA does not cover beta products or Free, Pro, Max, or Team plans.” A BAA is the business associate agreement a vendor signs before handling protected health information (PHI).
Anthropic’s test is one question: “will you be processing protected health information through Claude? If yes, you need the HIPAA-ready offering with a BAA.”
The document list has a small trap. A file called “2025 Type 1 HIPAA - Report (C4E)” is tagged “Claude for Work”, and that filter has no separate Team option. A Team customer can filter the page, see a HIPAA report and attach the wrong thing. I read C4E as Claude for Enterprise, and either way the table says N/A for Team.
If you handle PHI, you have two routes:
- Enterprise. The Primary Owner clicks through the BAA, and Anthropic warns “This is a one-way decision.” Connectors aren’t covered for data sent to third parties, and Cowork needs a further configuration only available with an account team, which the Cowork post covers.
- The API, inside software you build. Your Primary Owner signs a BAA, then contacts Anthropic to turn it on.
Otherwise, keep PHI out of Claude Team and write that rule down.
What should I write on the security questionnaire?
Copy these and change what isn’t true for you. Don’t write the bracketed parts unless you’ve done them.
| The question | What to write |
|---|---|
| Is your AI vendor SOC 2 Type II audited? | “Yes. Anthropic lists Claude Team in scope for SOC 2 Type 2 on its Trust Center. The latest published period is October 1, 2024 to September 30, 2025, with 2026 bridge letters available on request through the Trust Center.” |
| Are you SOC 2 compliant? | Answer for your own company. If you have no audit: “No. We have not had a SOC 2 examination. Our AI vendor has.” |
| Does that cover every feature you use? | “The listing is by plan. The published period predates Cowork, so we rely on [the bridge letter we reviewed] for it.” Or: “[Cowork is turned off for our organization.]” |
| Will you process PHI? Will you sign a BAA? | “Claude Team can’t enable HIPAA and isn’t covered by Anthropic’s BAA. [Our policy prohibits PHI in Claude.]” |
| Is our data used to train models? | “By default, we will not use your inputs or outputs from our commercial products” is Anthropic’s line. Thumbs up or down feedback is the exception, as is anything else you choose to allow. On Team you can also write “[we have disabled feedback for members].” |
| Do you keep audit logs of AI use? | “Not through Anthropic’s audit logs or Compliance API, which are Enterprise only.” Add whatever you do keep. Team owners can stream Cowork events to their own tools, though Anthropic says that “doesn’t replace audit logging for compliance purposes.” |
| Who are the subprocessors? | Link the list, which is more current than a copy. |
| What about third-party integrations? | List each connector, its owner and what it can write. Anthropic’s report doesn’t speak for Intuit or Google, and the directory says “Anthropic does not control which tools developers make available”. |
For that last row, start with the table of what 33 connectors can change. On Team, an owner can set tools to “Always allow, Needs approval, or Blocked.” If you have no written rule yet, use the one-page connector policy.
How do I get Anthropic’s SOC 2 report?
Go to the Trust Center, click the request access button and fill in the form. The reasons on offer include “I’m an existing customer” and “I’m a prospective customer.”
Ask for the 2025 SOC 2, the newest bridge letter and the prefilled questionnaire your customer’s format matches. The resources page lists a SIG Lite, CAIQ Full, VSA Core and HECVAT, all dated June 2026.
The SOC 3 is open to anyone, though its cover says “Unauthorized use, reproduction, or distribution of this report, in whole or in part, is strictly prohibited.” Send the link instead of attaching the PDF.
What I couldn’t confirm
- Whether the full SOC 2’s system description names Team, Cowork or connectors. The SOC 3 doesn’t. Read that section first.
- What the three bridge letters say, and whether any of them mention Cowork.
- Whether the full SOC 2 covers the same dates as the SOC 3. Both are filed as the 2025 Type 2.
- When the next report lands. Last year’s was signed November 12, 2025, and I found no published date.
- Whether you may forward the access-only documents to your customer. Check the terms when you get them.
What should I do before I send it back?
Check two things: whether anyone does company work outside a company seat (ask them), and whether Cowork is on for your organization. It’s on by default, and an owner can turn it off in Organization settings > Cowork. Then request the report and read its system description.
If you’d rather plan which of your tools to connect, and how, the setup planner asks six questions and gives you a plan without asking for an email. If you want a second look at an answer before it goes to a customer, bring the questionnaire to a 30-minute call.