Is It Safe to Connect Claude to Ramp?
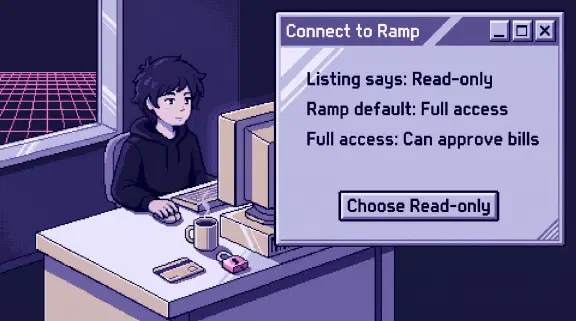
Safe enough if you choose Read-only on Ramp’s sign-in screen. The default is Full access, which can approve bills, unlock cards and get card credentials to buy things. Claude’s directory calls this connector read-only. Ramp’s own guide describes a lot more.
I haven’t tested this connector. Everything here comes from public pages I read on October 31, 2026.
The listing in Claude’s directory says it “Enables secure, read-only access to Ramp data” and shows 17 tools. Ramp’s guide says the consent screen “asks you to choose Full access (the default) or Read-only.” The table of what 33 connectors can change compares it with your other apps.
Is Claude’s Ramp connector read-only?
Only if you pick that. The listing and Ramp’s docs describe two different products:
| Claude’s listing | Ramp’s docs | |
|---|---|---|
| What it does | “read-only access to Ramp data” | “query Ramp data and take actions” |
| Address | ramp-mcp-remote.ramp.com/mcp | mcp.ramp.com/mcp |
| Tools | 17, such as load_cards | 224 in the reference, such as ramp_approve_or_reject_bill |
| Default access | Not mentioned | Full access |
Both point at the same connector. Ramp’s connection page sends Claude users to the same directory entry that the listing’s “Add to Claude” button opens.
None of the 17 listed names appears in Ramp’s tool reference, which calls itself the “canonical generated list” for Ramp’s server. The listing reads like an older design. Ramp’s archived server, with no code pushed since March 2025, loaded data into “a simple ETL pipeline + ephemeral sqlite database” and had execute_query and clear_table too.
The listing’s address also publishes the same 53 permission names as Ramp’s current one, including approvals:write and cards:write. That’s an odd list for a read-only server to advertise, though Ramp says its connections don’t use those scopes to limit access. Ignore the listing’s description and judge the connection by what you chose when you signed in.
What does each access level let Claude do?
Two things decide it: the access level you pick and your Ramp role. The access level comes first, from Ramp’s guide and help page:
| What Claude can do | Read-only | Full access (default) |
|---|---|---|
| Read spend, vendors, org chart, treasury balances | Yes | Yes |
| Edit memos and coding, submit reimbursements, post comments | No | Yes |
| Approve or reject transactions, bills, reimbursements, requests | No | Yes, if you’re an approver |
| Lock, unlock or activate cards | No | Yes |
| Get Agent Card credentials to buy something | See my list below | Yes, with an eligible fund |
Ramp enforces Read-only on its side. Its authorization guide says those connections don’t list tools that make changes, and write requests “fail with 403 Forbidden”. To change level, you reconnect.
Your role sets the size of the blast. Ramp’s guide says “Employees see their own data; admins can see company-wide data.” A finance admin on Full access is the connection to worry about. The reference has ramp_issue_one_off_funds, which issues funds “bypassing approval flows” for someone holding that permission.
Can Claude approve a bill and trigger a payment?
On Full access, yes, and I’d show this line to whoever runs finance. Ramp’s help page says: “Approving a bill can cause it to proceed to payment automatically when it becomes fully approved, payment details and a payment date are already set, and your company’s payment-release settings allow it.”
There are limits. The reference says the bill tool “never schedules payments or edits payment details”, and that “Some bills require step-up verification that agents cannot complete”. You still need to be the next approver. But if the last signature is yours, Claude can sign it.
Ramp’s sample prompts lean into this. One reads “Approve all transactions under $100 that have a clear business memo.” Its approval instructions for agents say “Never blind-approve” and “Confirm with the user before executing approvals”. That’s guidance written for the model. I found nothing saying Ramp’s server enforces it.
The card tool has its own version of this. Its description tells the agent to lock a card only on a clear request, then adds: “Unlocking does not require additional confirmation.”
Can Claude spend money on a Ramp card?
On Full access, with the right fund, yes. Ramp’s guide lists “Make purchases: get Agent Card credentials.” Its payments page says no separate agent identity is needed, and “The agent can use the cards, funds, and permissions that are already available to the Ramp user who connected it.”
The tool, ramp_get_agent_card_creds, needs a fund, a merchant and an amount. The payments page says it’s for a browser checkout. A purchase follows “the fund’s spend limit, merchant rules, approval policies, and accounting defaults”, so the fund is your brake. The same page says the agent confirms the merchant and total first. That step lives in Ramp’s instructions for the model. Keep small limits and merchant rules on any fund a connected person can reach.
The reference also has ramp_pay_with_x402, which pays from “your business’s stablecoin balance”. That wallet is funded separately, and Ramp warns: “do not assume that card or fund controls apply identically to this method.”
Can an invoice trick Claude?
Yes. Finance data is full of text other people wrote. Vendors write invoices, and the reference has a tool that fetches “invoice file attachments” as a download link. A hidden instruction in one is called a prompt injection. Anthropic’s Cowork safety page says one works when “Claude can read information outside your trusted boundary, and can perform actions that could compromise the user.” Anthropic also says it trains Claude to detect these attacks. Full access meets both conditions. Read-only removes the second inside Ramp, but not if the same chat has another connector that can send.
Who controls this at my company?
Two sets of admins, and neither controls the whole thing.
In Ramp, an admin decides who can connect: company-wide or for specific users on all plans, per role on Ramp Plus. The access level is picked per connection. The controls Ramp documents cover who can connect, and I found none that sets the access level. The Connected AI tools page shows “who connected each one, its status, and when it was last used”, but only when that review is enabled for your business. Its description doesn’t mention access level. It’s “a read-only overview”, so you can’t remove a connection there. A connection in use “stays active and re-authenticates in the background.”
In Claude, an owner on Team or Enterprise can set each tool to “Always allow, Needs approval, or Blocked”, and “individual users can’t override it.” That’s how you enforce this. In Customize, then Connectors, block whichever approval, unlock and credential tools appear for the whole company, whatever someone clicks on Ramp’s screen.
Can admins see what Claude did in Ramp?
Partly. Ramp says it “attributes MCP calls to the employee who connected the tool”, and its audit log shows individual changes “only when that action normally creates an audit event.” So plan on a Claude approval looking like that person’s approval.
One controller in Ramp’s own blog post about month-end wants to run as much of his close through Claude as he can and still “doesn’t approve or release payments through AI”. He keeps that in Ramp’s product, “where there’s a full audit trail.” I’d copy him.
Does Claude train on your Ramp data?
Not by default on Team or Enterprise. Anthropic says “we will not use your inputs or outputs from our commercial products”, unless you report feedback. On personal plans it’s a setting you choose, and training data “does not include raw content from connectors”, though it can include what’s “directly copied into your conversation with Claude.” A summary of your spend that Claude writes back is your conversation. Keep company finance data on a company plan.
How do I connect Claude to Ramp safely?
- Limit who can connect. In Ramp, open Integrations, select Ramp MCP, then Manage access. Start with one named person.
- Check your payment-release settings before any approver connects, so you know whether a final approval pays the bill.
- Choose Read-only on the consent screen. If you don’t see the choice, stop and find out why. Ramp’s help page suggests asking the assistant to “Run ramp_token_info” to explain restrictions on the connection.
- Test it. Ask Claude to list its Ramp tools, then ask it to add a test memo to one of your own transactions. On Read-only, Claude shouldn’t have a tool for that, and any write that reaches Ramp fails with error
DEVELOPER_7100. - Set the tools in Claude, with an owner doing it for the organization. Approvals, unlocks and card credentials get Blocked or Needs approval.
- Try Full access on sample data first, if someone needs it. Ramp’s guide offers
https://demo-mcp.ramp.com/mcp, and its help page says that address is for sandbox accounts, so you’ll need one. - Write down who connected, and at which level. Ramp’s page may not tell you the second part later.
What I couldn’t confirm
- Which tools Claude shows after sign-in: the listing’s 17, some of Ramp’s 224, or both. Both addresses refuse without a login.
- Whether connecting through Claude’s directory always shows the access choice. The guide says the screen “asks”, and the help page says “When the authorization screen offers” it.
- Whether Read-only hides Agent Card credentials. The tool’s name starts with “get”, and Ramp’s published permissions include
cards:read_agentic. Look for it in step 4. - Whether a card number reaches the chat. The tool description says “one-time payment token”, while the checkout instructions mention “returned card details”.
- Whether Ramp’s audit log marks an action as made through Claude. The reference has an
agent_namesfilter, and I couldn’t see what it returns for a person’s connection.
Should I connect Claude to Ramp?
Yes on Read-only. Asking about spend, vendors and missing receipts in plain English is the useful part for most companies, and by Ramp’s account that level can’t change anything. I’d keep approvers off Full access until someone owns the settings above. For the rules around it, use the one-page connector policy in the QuickBooks post. Stripe’s listing has a similar gap between what it says and what its tools do.
If you’d rather plan which of your tools to connect, and how, the setup planner asks six questions and gives you a plan without asking for an email. If you want a second look at a list you already have, bring your connected apps to a 30-minute call.